Our consulting is characterized by quality and security

Conceptual IT-Consulting

on highest level
text icon

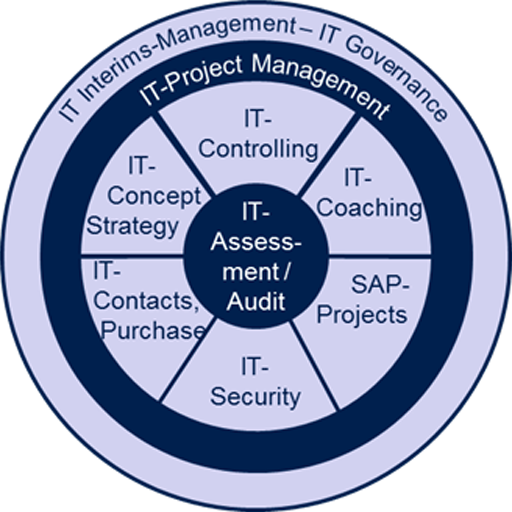
IT-Assessment/IT-Audit

Document and analyze existing IT environment, risks and weaknesses based on ISO27001.
text icon

IT-Concept/-Strategy Development

Develop IT Strategies and Concepts based on findings in the risk assessment analysis. Develop a future IT strategy.
text icon

IT-Security

Analysis and review, as well as consulting regarding the IT-Security standard ISO27001.

what do we deliver?

We offer a broad variety of international all industry concerning “IT Executive Management” consulting.

how do we deliver?

Our Senior-Consultants hold a minimum experience of 15 years in leading IT-organizations and generate tailor-made management functions for your enterprise.

why do we deliver?

We focus on control and optimization of the IT based on company strategy and regarding efficiency, cost/value and security.

IT-Assessment/IT-Audit

Purpose of the IT-Assessment is the collection of information and their documentation of the environment and the systems supporting the information processing and their neutral risk evaluation and the generation of a priority list of remedial actions. IT-systems are being reviewed from a technical as well as from an administrative point of view. The analysis approach comply with the IT security normative ISO27001. In the run-up the Content and the level of detail are being aligned with the initiator. The findings of the IT-Assessment serve also as a neutral validation of the current IT situation. It can be applied as a presentation in the face of third-party (e.g. preparation for an ISO27001 audit) as well as a baseline for a master plan to improve IT or for a short-term takeover of a temporary IT management.

The practice of the analysis is generally composed by the following steps:

Analyse Data collection Interview Validation Generation Derivation Presentation

1 . Analysis of IT organization and IT Budget

IT Analysen

IT-Concept/-Strategy Development

Not having a IT strategy in many companies leads to “momentum” and ” uncontrolled growth” in IT infrastructure and organization, which could results in the following aberrations:

  • dependencies on IT personnel
  • influence of “prince of department”
  • No overview of applied HW, SW and infrastructure
  • No clear borderline of responsibilities
  • incorrect budget
  • No IT controlling
  • NO IT contract overview
  • incomplete or non-controlled security rules

In order to control the IT within the meaning of the company a IT strategy which economically rules the IT organization, service processes and applied Infrastructure (HW, SW, network) is mandatory. From the findings of the preceding IT-assessment in conjunction with the objectives of the IT department and the company-strategy concepts and strategies for the information processing can be derivated.

IT-Security

Analysis and review, as well as consulting regarding the IT-Security standard ISO27001.

Contact Details

let’s keep in touch